
A security vulnerability has been detected in the popular WordPress plugin!
As technology has advanced significantly in recent years, new cyber attack methods have emerged. Although companies release updates that close the vulnerabilities against these methods, a new vulnerability may be created while trying to close the vulnerabilities with these updates. According to…
 Emir Bolat
Published Updated 1 min read
As technology has advanced significantly in recent years, new cyber attack methods have emerged. Although companies release updates that close the vulnerabilities against these methods, a new vulnerability may be created while trying to close the vulnerabilities with these updates. According to recent developments, approximately 1 million websites are in danger due to a WordPress plugin. Here are the details…
A vulnerability was discovered in the WordPress Website Builder plugin
According to a report published by the developers of Wordfence, the WordPress security plugin used on almost every website, a security vulnerability was discovered in the Website Builder plugin developed by SeedProd , which has more than 900 thousand active installations .
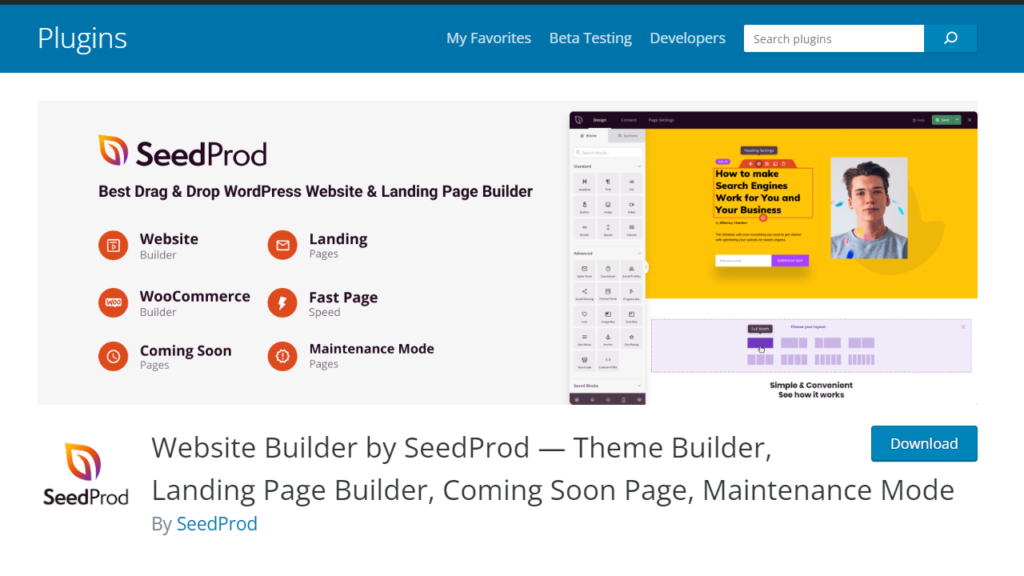
According to the information transferred, hackers can change the content of the pages with this vulnerability, which is defined as high risk. In this context, we can say that there is a serious weakness. This vulnerability, which was said to be in version 6.15.21, was closed when the developer company released the update version 6.15.22. In this context, if you are using this plugin on your website, we recommend that you update it.
Steam put an end to the Intel vs AMD debate! Here is the data
WordPress is used on 43 percent of all websites on the internet. In this regard, it also attracts the attention of hackers. The system also makes a name for itself with its reliability. For this reason, when searching for vulnerabilities on a WordPress site, vulnerabilities are usually looked for in plugins.
Especially after being developed and published by a developer, the possibility of vulnerabilities are quite high in plugins that have not received updates for years. In this context, it is beneficial to choose plug-ins that are constantly updated.
So what do you think about this issue? You can share your opinions with us in the Comments section below.